Securepoint UTM v14
Securepoint UTM v14BSI zaleca — stan na 01.2025 — długości kluczy od 3000 bitów i SHA256
BSI – Wytyczne techniczne — Metody kryptograficzne: Zalecenia i długości kluczy BSI TR-02102-1 | Rozdział 2.3: Szyfrowanie RSA
Domyślne ustawienie UTM dla nowych certyfikatów to klucz RSA o długości 3072 bit oraz SHA256 jako algorytm hashujący
Build 14.2.1.1 Wersja beta
| Data premiery: | 30.10.2026 | Dostępne do pobrania w Reseller Portal (RSP) | ||
| Aktualizacja online: | wkrótce | Planowany przedział czasowy wdrożenia: | 1 | dzień |
| Terra Cloud: | - | Planowany przedział czasowy wdrożenia: | 3 | dni |
Głównym celem tych wersji jest uzyskanie cennych opinii od naszych partnerów. Opinie te zostaną uwzględnione w ostatecznej wersji naszego oprogramowania, zanim zostanie ono udostępnione dla wszystkich użytkowników.
Dziękujemy wszystkim partnerom za wsparcie i wkład w optymalizację naszego oprogramowania.'
Ta wersja nie jest przeznaczona do użytku w środowiskach produkcyjnych
- Poprawki błędów związanych z bezpieczeństwem
- Aktualizacja pakietu certyfikatów CA
- Aktualizacja kernela
Build 14.1.9.7
| Data premiery: | 30.10.2026 | Planowany przedział czasowy wdrożenia: | 5 | dni |
| Terra Cloud: | 30.10.2026 | Planowany przedział czasowy wdrożenia: | 3 | dni |
- Konserwacja / Bezpieczeństwo – poprawki błędów
- Aktualizacja kernela
Build 14.1.9.6
| Data premiery: | 26.10.2026 | Planowany przedział czasowy wdrożenia: | 5 | dni |
| Terra Cloud: | 26.10.2026 | Planowany przedział czasowy wdrożenia: | 3 | dni |
- Poprawki błędów związanych z bezpieczeństwem
- Aktualizacja pakietu certyfikatów CA
Build 14.1.9.5
| Data premiery: | 15.10.2026 | Planowany przedział czasowy wdrożenia: | 6 | dni |
| Terra Cloud: | 15.10.2026 | Planowany przedział czasowy wdrożenia: | 3 | dni |
- Funkcja
- Za pomocą CLI można ustawić parametr interfejsu gso_max_size, aby ograniczyć maksymalny rozmiar pakietów przekazywanych do interfejsu sieciowego, w przypadku problemów z transmisją pakietów: Wiki
Build 14.2.1 Wersja beta
| Data premiery: | 12.10.2026 | Planowany przedział czasowy wdrożenia: | 1 | dzień |
| Terra Cloud: | - | Planowany przedział czasowy wdrożenia: | 3 | dni |
Głównym celem tych wersji jest uzyskanie cennych opinii od naszych partnerów. Opinie te zostaną uwzględnione w ostatecznej wersji naszego oprogramowania, zanim zostanie ono udostępnione dla wszystkich użytkowników.
Dziękujemy wszystkim partnerom za wsparcie i wkład w optymalizację naszego oprogramowania.'
Ta wersja nie jest przeznaczona do użytku w środowiskach produkcyjnych
- Konserwacja / Poprawki błędów bezpieczeństwa
- Usunięcie luki w zabezpieczeniach serwera proxy IGMP
- Aktualizacja serwera reverse proxy nginx do wersji 1.31.3
- Aktualizacja komponentu w usłudze DNS
- CVE-2026-33278 / EUVD-2026-31075
- CVE-2026-77860 / EUVD-2026-80286
- CVE-2026-77955 / EUVD-2026-80287
- CVE-2026-78227 / EUVD-2026-80288
- CVE-2026-80225 / EUVD-2026-80289
- CVE-2026-81634 / EUVD-2026-80290
- CVE-2026-81642 / EUVD-2026-80291
- CVE-2026-82717 / EUVD-2026-80292
- CVE-2026-82720 / EUVD-2026-80293
- CVE-2026-85501 / EUVD-2026-80294
- Aktualizacja biblioteki OpenSSL do wersji 3.5.7. Certyfikaty z podpisami SHA1 są teraz klasyfikowane jako poziom bezpieczeństwa 0 (CVE-2026-84782 / EUVD-EUVD-2026-89013)
- Aktualizacja systemu skanowania wirusów
- Aktualizacja usługi SSH OpenSSH do wersji 10.5p1
- Aktualizacja serwera HTTP proxy (Squid) do wersji 7.6
- Funkcje
- Wybór kolumn w wyszukiwaniu zaawansowanym został ulepszony, dzięki czemu łatwiej jest rozróżnić wielokrotnie występujące nazwy kolumn
- Kolory i opisy etykiet w kwarantannie poczty zostały dostosowane, aby zapewnić lepszą czytelność: Wiki
- Przycisk pobierania informacji dotyczących pomocy technicznej został przeniesiony do paska narzędzi w lewym dolnym rogu ekranu: Wiki
- Użytkownikom FreeOTP wyświetlane jest teraz logo Securepoint w przypadku połączeń Securepoint VPN, aby zapewnić lepszą rozpoznawalność: Wiki
- W interfejsie administratora i interfejsie użytkownika można teraz pobrać konfigurację WireGuard wraz z instalatorem klienta VPN, nawet jeśli SSL VPN nie jest skonfigurowany: Wiki
- W SSL VPN wyświetlany jest status zdalnych klientów: Wiki
- W sieci SSL-VPN połączenie klienckie typu S2S można teraz ręcznie rozłączyć, aby klient przejął zmienione ustawienia poprzez ponowne nawiązanie połączenia: Wiki
- W kroku 8 kreatora instalacji wymagane jest podanie nazwy miasta
- W instrukcji dotyczącej nowej instalacji UTM dodano informacje na temat rejestracji pakietów oraz wylogowywania się. Usunięto kroki, które nie są już konieczne.
- Za pomocą polecenia CLI można ustawić preferowany tryb pracy modemu w sieci komórkowej
- Domyślnie aktywny agent LLDP w kartach sieciowych Intel X710 zostaje wyłączony, ponieważ sprzętowe przetwarzanie ramek LLDP może powodować problemy z LACP, agregacją łączy i bondingiem
- Podczas konfiguracji połączeń OAuth2 można wybierać wyłącznie certyfikaty RSA
- Poprawki błędów
- Skanowanie bezpieczeństwa za pośrednictwem USP znów działa dla urządzeń UTM, które mają skonfigurowanych kilka publicznych adresów IP
- Otwieranie sesji internetowej z poziomu USP zostało zoptymalizowane pod kątem mniejszej przepustowości łącza internetowego
- Konfiguracja HTTP proxy oparta na interfejsie mogła powodować błąd, jeśli adres IP został usunięty z danego interfejsu
- Naprawiono sporadyczne, niepożądane wylogowania z interfejsu administracyjnego
- Po włączeniu funkcji wykrywania podobieństw port 8083 był błędnie dostępny z zewnątrz
- W niektórych przypadkach aktualizacja oprogramowania sprzętowego kończyła się niepowodzeniem z powodu nieprawidłowo skonfigurowanej reguły
- Naprawiono błąd w serwerze Mailrelay podczas sprawdzania adresów e-mail dla folderów publicznych w Exchange
- Podczas korzystania z transparentnego HTTP Proxy z profilem konfiguracyjnym dochodziło do powtarzających się restartów Squid proxy
- Sieć VPN bez klienta działa teraz również dla użytkowników Entra ID, którym nie przypisano imienia (givenName)
- Połączenia IPsec typu Roadwarrior z pulami DHCP znów działają niezawodnie, jeśli pula znajduje się w sieci wybranego interfejsu
- Anonimizację można znów niezawodnie wyłączyć
- Podczas pracy przy peer Wireguard z prefiksem /32 jest on poprawnie wyświetlany i zapisywany
- W maintenance console akceptowane są teraz również hasła zawierające więcej niż 33 znaki
- W kreatorze instalacji ustawienie dotyczące ochrony danych dla reverse proxy nginx jest ponownie prawidłowo konfigurowane
Known_issue
- Known Issue
| Component: | SSL-VPN with OTP | Opis | SSL-VPN with OTP does not work with Securepoint Windows VPN Client versions ≤ 3.6.2 | Solution: | With the Windows VPN Client from v3.6.3 onwards, SSL-VPN connections are also possible with OTP. The client is available as an automatic update, via the reseller portal (RSP) or on Github |
Build 14.1.9.3
| Data premiery: | 01.10.2026 | Planowany przedział czasowy wdrożenia: | 5 | dni |
| Terra Cloud: | 08.10.3036 | Planowany przedział czasowy wdrożenia: | 3 | dni |
- Konserwacja / Poprawki błędów związanych z bezpieczeństwem
- Aktualizacja biblioteki OpenSSL (CVE-2026-84782 / EUVD-2026-89013)
- Poprawki błędów
- Poprawiono stabilność podczas przełączania na główny moduł UTM w klastrze oraz podczas późniejszej reaktywacji aplikacji
Build 14.1.9.2
| Data premiery: | 23.09.2026 | Planowany przedział czasowy wdrożenia: | 5 | dni |
| Terra Cloud: | 28.09.2026 | Planowany przedział czasowy wdrożenia: | 3 | dni |
- Konserwacja / Bezpieczeństwo – poprawki błędów
- sunięcie luk w zabezpieczeniach serwera nazw
- Aktualizacja jądra
Build 14.1.9.1
- Release Date: 11.09.2026
- Planowany przedział czasowy wdrożenia: 5 dni
- Terra Cloud: 18.09.2026
- Planowany przedział czasowy wdrożenia: 3 dni
- Poprawki błędów
- Podczas odnawiania certyfikatów ACME mogły wystąpić błędy, zwłaszcza w przypadku stosowania wielu alternatywnych nazw podmiotu (SAN) i aliasów (CNAME)
- W przypadku jednorazowej aktualizacji za pośrednictwem Unified Security Portal umowa EULA jest teraz automatycznie akceptowana nawet w przypadku pominięcia wersji UTM, dzięki czemu do sfinalizowania procesu nie są wymagane żadne dodatkowe działania ze strony użytkownika
Build 14.1.9
- Release Date: 26.08.2026
- Planowany przedział czasowy wdrożenia: 14 dni
- Terra Cloud: 26.08.2026
- Planowany przedział czasowy wdrożenia: 3 dni
- Bug Fixes
- Jeśli filtr internetowy był wyłączony, mogło to spowodować, że przezroczysty serwer proxy nie działał
Build 14.1.8
- Release Date: 05.08.2026
- Planowany przedział czasowy wdrożenia: 14 dni
- Terra Cloud: 06.08.2026
- Planowany przedział czasowy wdrożenia: 3 dni
- Bug Fixes
- Gdy wykrywanie podobieństwa było włączone, port 8083 był nieprawidłowo dostępny z zewnątrz
- Maintenance / Security Bug Fixes
- Naprawiono lukę bezpieczeństwa w bibliotece („HollowByte” – podatność typu DoS)
- Naprawiono luki bezpieczeństwa w rozwiązaniu Clientless VPN (CVE-2026-32853, CVE-2026-32854)
- Zaktualizowano komponent filtra poczty
Known_issue
- Known Issue
| Component: | HTTP-Proxy | Opis: | W niektórych środowiskach może się zdarzyć, że strony internetowe nie będą się już ładować przez serwer proxy HTTP, jeśli filtr internetowy jest wyłączony | Workaround: | Włącz filtr internetowy lub przywróć wersję 14.1.7 lub starszą |
Build 14.1.7
- Release Date: 21.07.2026
- Planowany przedział czasowy wdrożenia: 14 dni
- Terra Cloud: 31.07.2026
- Planowany przedział czasowy wdrożenia: 3 dni
- Maintenance / Security Bugfixes
- Zaktualizowano usługę serwera DNS (nameserver) (CVE-2026-33278 / EUVD-2026-31075)
- Zaktualizowano HTTP Proxy (Squid) (CVE-2026-47729 / EUVD-2026-44962)
- Zaktualizowano OpenVPN do wersji 2.6.21
- Security Bugfixes
- Poprawiono stabilność i kompatybilność z wybranymi wersjami oprogramowania sprzętowego (firmware) modemów sieci mobilnej
- Przywrócono prawidłowe działanie reguł filtrowania pakietów wykorzystujących grupy IBF
- W rzadkich przypadkach status synchronizacji klastra był nieprawidłowo raportowany jako asynchroniczny
- W rzadkich przypadkach podczas aktualizacji z bardzo starych wersji UTM oraz podczas importu konfiguracji występowały błędy w procesie aktualizacji
- Usunięto problem z wyświetlaniem komunikatów dziennika (logów) SSL VPN
Build 14.2.0 Wersja beta
- Data premiery: 06.07.2026
- Planowany przedział czasowy wdrożenia: 1 dzień
- Dostępne wyłącznie dla urządzeń z włączoną funkcją aktualizacji beta
- Terra Cloud: -
Głównym celem tych wersji jest uzyskanie cennych opinii od naszych partnerów. Opinie te zostaną uwzględnione w ostatecznej wersji naszego oprogramowania, zanim zostanie ono udostępnione dla wszystkich użytkowników.
Dziękujemy wszystkim partnerom za wsparcie i wkład w optymalizację naszego oprogramowania.'
Ta wersja nie jest przeznaczona do użytku w środowiskach produkcyjnych
- Nowe funkcje
- Interfejsy administratora i użytkownika UTM są teraz również dostępne w języku polskim (eksperymentalnie). Język nie zmienia się automatycznie na podstawie ustawień przeglądarki. Użyj parametru URL "lang=pl-beta".
Na przykład: https://192.168.175.1:11115/?lang=pl-beta Wiki - Moduł bezpieczeństwa można teraz ustawiać w oknie dialogowym szyfrowania. W oknie certyfikatów, certyfikaty niespełniające określonego poziomu bezpieczeństwa bedą oznaczane, jeśli zostało to odpowiednio skonfigurowane: Wiki
- Specyficzna funkcja wyszukiwania dla kolumny jest teraz dostępna we wszystkich oknach dialogowych zawierających tabele: Wiki
- Features
- Cluster
- W klastrze konfiguracje głównego i drugorzędnego klastra są teraz dostępne do pobrania na obu urządzeniach: Wiki
- Archiwum poczty jest teraz synchronizowany na obu maszynach w klastrze
- Aby ułatwić przejście z istniejących UTM do klastrowych UTM, użytkownicy mogą teraz tworzyć wirtualne adresy IP dla wielu interfejsów lub konwertować istniejące adresy IP w kreatorze klastra: Wiki
- HTTP Proxy
- Profile konfiguracji proxy HTTP wyświetlają teraz wszystkie wartości odziedziczone z globalnego profilu konfiguracji
- Rozszerzono funkcję rejestrowania danych z pamięci podręcznej (cache) serwera HTTP proxy. Logi debugowania można teraz włączać osobno dla wybranych obszarów i poziomów szczegółowości, aby ułatwić analizę skomplikowanych lub sporadycznych problemów związanych z serwerami proxy. Wiki
- W serwerze proxy HTTP można skonfigurować liczbę wątków (threads): Wiki
- Filtr poczty
- Przy ponownym wysyłaniu wiadomości e-mail z kwarantanny jako nadawca jest teraz używany globalny adres e-mail administratora
- W ustawieniach filtra poczty można skonfigurować, czy i kiedy wiadomość e-mail ma zostać ponownie sprawdzona, jeśli podczas pierwszego przetwarzania wystąpił błąd
- Podczas dodawania reguł filtrowania w filtrze poczty można rozróżnić nadawcę technicznego od nadawcy widocznego: Wiki
- Mailrelay
- Wynik DKIM „policy” może być używany w regułach filtrowania. Ponadto można indywidualnie skonfigurować akceptowane algorytmy DKIM oraz minimalną długość klucza: Wiki
- Wymagania TLS można konfigurować dla każdej domeny/nazwy hosta: Wiki
- Filtr pakietów
- Do listy wstępnie skonfigurowanych usług został dodany QUIC na porcie 443
- Konfiguracja sieci
- W filtrze pakietów adres MAC został przeniesiony z podpowiedzi do rozwijanego okna zawierającego szczegółowe informacje:Wiki
- W konfiguracji sieciowej, interfejsy typu Ethernet, Bond, Bridge, VLAN i WLAN mogą być teraz konfigurowane z dwoma adresami RDNSS, gdy włączone są funkcje Router Advertisement i Przydzielanie adresów IPv6: Wiki
- WireGuard
- Konfiguracja WireGuard obsługuje teraz zakres wartości portów od 1 do 65535
- Podczas tworzenia nowego połączenia WireGuard zaawansowane ustawienia (strefy i obiekty sieciowe) można teraz konfigurować również dla użytkowników AD i użytkowników lokalnych — podobnie jak dla peerów: Wiki
- Pulpit
- Wartość bieżącego punktu danych w widżecie "Obciążenie" jest wyświetlane jako prędkościomierz: Wiki
- Widżet "Interfejs" został rozbudowany o możliwość wyboru typu danych: Wiki
- Kreator konfiguracji
- W kreatorze konfiguracji podczas tworzenia połączenia modemowego PPPoE lub DHCP serwer DNS dostawcy jest automatycznie używany, aby zapobiec problemom z rozwiązywaniem nazw. W razie potrzeby tę opcję można wyłączyć: Wiki
- W drugim kroku kreatora konfiguracji (teraz nazywanym „Ustawienia zabezpieczeń”) można teraz również skonfigurować używanie filtra Threat Intelligence i GeoIP: Wiki
- Przy pierwszym logowaniu do nowegeo urządzenia UTM można teraz bezpośrednio zaimportować już istniejącą konfigurację: Wiki
- Można teraz konfigurować, które reguły filtra pakietów powinny być tworzone automatycznie: Wiki
- Webinterface
- Opcje „Uruchom ponownie” i „Wyłącz” są teraz dostępne w menu podręcznym pod pozycją menu „Wyloguj się”: Wiki
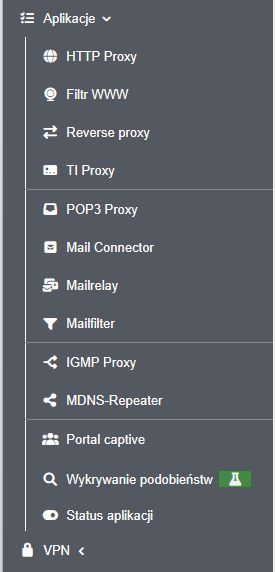
- Zawartość sekcji „Aplikacje” została ponownie posortowana i pogrupowana, aby lepiej odzwierciedlić logiczne powiązania Funkcja "IDS/IPS" została przeniesiona do menu „Zapora sieciowa” a sekcja "Ustawienia DNS" do zakładki „Sieć”
- Urządzenia UTM w klastrze są teraz oznaczane jako "główny" i "drugorzędny" lub — w zależności od ich statusu — "aktywny" i "pasywny": Wiki
- Komunikat ostrzegawczy jest teraz wyświetlany podczas przechodzenia do innej strony, jeśli istnieją niezapisane lub nieprawidłowe wpisy. W razie potrzeby ten komunikat można wyłączyć w ustawieniach zaawansowanych: Wiki
- Podczas dodawania połączenia OAuth2 można tworzyć certyfikaty bez konieczności wychodzenia z okna dialogowego dodawania: Wiki
- Ulepszono nazwy opcji pobierania w oknie dialogowym SSL-VPN: Wiki
- Od teraz można kopiować w tabelach obiektów sieciowych, usług, profili filtra internetowego, ClientlessVPN i użytkowników

- Inne
- Minimalna długość nowo tworzonych kluczy została zwiększona do 2048 bitów: Wiki
- Usługi wyłączone w konfiguracji klastra są ponownie włączane, gdy konfiguracja jest importowana do urządzenia bez licencji klastra
- Wygląd raportu dotyczącego Spamu został unowocześniony i została poprawiona jego responsywność: Wiki
- W przypadku typu katalogu Entra ID można teraz skonfigurować rozszerzone nazwy atrybutów w uwierzytelnianiu AD/LDAP: Wiki
- Nieznane nazwy w strefie Forward DNS mogą być teraz opcjonalnie rozwiązywane za pośrednictwem zewnętrznych serwerów nazw, aby poprawić zgodność z zewnętrznymi celami CNAME: Wiki
- Podczas rejestracji zero-touch UTM za pośrednictwem USP przeprowadzana jest aktualizacja do najnowszej wersji UTM nawet bez dołączonej konfiguracji: Wiki
- Bug fixes
- Podczas tworzenia obiektów sieciowych typów „Host VPN” i „Sieć VPN” wszystkie strefy związane z VPN są teraz poprawnie wyświetlane.
- Numery seryjne licencji są teraz poprawnie wyświetlane w zapytaniach SNMP
- Wydruk lokalnej konfiguracji (w zarządzaniu konfiguracją) uzupełniono o brakujące wartości dla strefy Relay DNS, IDS/IPS i centrum alertów
- Kolejność wpisów SAN w certyfikacie ACME nie może być już zmieniana, aby zapewnić integralność certyfikatu
- W logch filtra pakietów, nie pojawiają się już tymczasowe wpisy ACCEPT, przed ostatecznym odrzuceniem żądań do celów zablokowanych systemowo
- Karty pomocy online i log są automatycznie zamykane, gdy tylko zostanie zamknięte główne okno interfejsu UTM
Known_issue
- Known Issue
| Component: | Nazwy interfejsów | Opis: | Podczas importowania pliku konfiguracyjnego nowo zainstalowanego i jeszcze nielicencjonowanego urządzenia UTM nazwy interfejsów ze schematu LAN nie są poprawnie dostosowywane do schematu A/B/C (przykład: LAN1 → A1), co powoduje, że po ponownym uruchomieniu urządzenia nie można uzyskać dostępu do tych interfejsów. Z wyjątkiem sprzętu G5 i G6, problem z schematem LAN występuje we wszystkich systemach. |
Workaround: | Po zainstalowaniu i aktywowaniu licencji nowego urządzenia UTM należy zaimportować plik konfiguracyjny za pomocą narzędzia do zarządzania konfiguracją |
Build 14.1.6
- Release Date: 16.06.2026
- Planowany przedział czasowy wdrożenia: 14 dni
- Terra Cloud: 24.06.2026
- Planowany przedział czasowy wdrożenia: 3 dni
Maintenance / Security Bugfixes
- Fixed security vulnerabilities in the Linux kernel
- Fixed a security vulnerability in the nginx reverse proxy
- Updated OpenVPN to version 2.6.20
- Feature
- The "Redirect Gateway" parameter in the SSL-VPN section is set to “Off” by default for new users
- Bugfixes
- SSL-VPN: Adjusting the MSS-Fix value to 1450 resolved connection issues with certain services following OpenVPN updates
- The evaluation of cluster priorities has been corrected. After a failover, the device with the higher priority now automatically assumes the active role again as soon as both cluster nodes are available
- During a one-time update via the Unified Security Portal, the EULA is automatically accepted again, so no further action is required by the user to finalize the process
- The system-wide proxy is now used correctly again in the web filter
- When using the AUTH_GEN_TOKEN function, users were in rare cases assigned incorrect IPs during the OpenVPN connection
- The parameters for lease time and for rejecting unknown clients can be configured again for DHCP
- Segfaults in the nginx reverse proxy have been fixed
- The cluster configuration dialog can only be exited after the save process is complete to ensure that all parameters are fully saved
Build 14.1.5.1
- Release Date: 01.06.2026
- Planowany przedział czasowy wdrożenia: 14 dni
- Terra Cloud: 15.06.2026
- Planowany przedział czasowy wdrożenia: 3 dni
- In some cases in cluster environments, devices could no longer be reached via their virtual IP address
- A WAN interface can no longer be mistakenly configured as a cluster HA interface
Known_issue
- Known Issue
| Component: | Cluster activation | Opis | Currently, the priority on the passive machine is calculated incorrectly if interfaces are configured with the option Interface is disabled during backup. If one or a small number of interfaces fail, this may therefore lead to restrictions when switching between systems. |
Workaround: | Rollback to 14.1.4 or earlier |
Build 14.1.5
- Release Date: 19.05.2026
Planowany przedział czasowy wdrożenia: 14 dni
- Terra Cloud: -
- Maintenance / Security Bug Fixes
- Security vulnerabilities in the IPSec service have been addressed (CVE-2026-35328 / Strongswan), (CVE-2026-35329 / Strongswan), (CVE-2026-35331 / Strongswan), (CVE-2026-35332 / Strongswan)
- Features
- Obsolete hash algorithms in SSL-VPN are marked as “not supported” in existing configurations and cannot be selected anymore
- The Alerting Center will now notify users about certificates that use obsolete signature algorithms
- Bug fixes
- In the appliance view of the dashboard, an interface is now correctly displayed as active (with a green border) even when a fallback is configured
- The global email address in the server settings was incorrectly marked as invalid if parts of it resembled untrusted domains
- Segfaults in the keepalived process have been fixed
- Rare instances of high CPU usage caused by the TI proxy have been fixed
- The advanced setting “HTTP and Reverse Proxy File Descriptor” now also applies to the nginx reverse proxy
- Backups are now performed correctly for Hyper-V VSS configurations (Volume Shadow Copy Service)
- The UTM spam report is now MIME-compliant again and no longer triggers spam filters
- Resolution for URL shorteners in the web filter has been optimized. A tooltip provides information on the exact procedure
- LTE connection stabilized – the wwan interface now correctly re-establishes the IPv4 connection after a drop
- Cluster synchronization now works even if the maximum number of configurations has already been reached
Known_issue
- Known Issue
| Component: | Missing virtual IP addresses in cluster environments | Opis | In cluster environments, there may be instances where devices can no longer be reached via their virtual IP address | Workaround: | Rollback (or reboot, if the UTM is no longer accessible) |
Build 14.1.4
- Release Date: 07.04.2026
- Planowany przedział czasowy wdrożenia: 14 dni
- Terra Cloud: 23.04.2026
- Planowany przedział czasowy wdrożenia: 3 dni
- Features
- An error message in the network tools now alerts the user if domains to be checked contain errors when using the similarity detection
- Bug Fixes
- Due to a change in password processing for clusters, the primary and spare UTMs could switch to active mode simultaneously
- Fixed a critical issue that occurred if an AD server was unreachable during joining
- Fixed rare issues that occurred when downloading UTM configuration files, certificates, or VPN configurations
- Fixed a reverse proxy error, thereby reducing issues with NTLM
- Rules configured with NAT in the packet filter can now be edited again, even if no GeoIP network objects are present
- When selecting the NETMAP type in the NAT configuration, a network object can now be selected again
- Fixed a DynDNS error that caused functionality issues if the configured DynDNS resolver could not be reached via IPv6
- Exceptions for certificate verification are now correctly applied in the transparent proxy
- In isolated cases, trusted domains were blocked in the web filter by the similarity detection feature
- Only a small number of devices could be added to the TI proxy
- The IPS server now starts successfully again
- Older UTM systems could encounter issues during cluster synchronization
- Regex patterns were not saved correctly for newly created email filter rules
- Some mobile connections were terminated after a short time
Build 14.1.3
- Release Date: 09.03.2026
- Planowany przedział czasowy wdrożenia: 14 dni
- Terra Cloud: -
- Features
- Multi-factor authentication with Entra ID via SSL VPN (OpenVPN) using OpenID Connect (OIDC) is now supported for all standard OpenVPN clients
- Domain blocking triggered by similarity detection can now be temporarily bypassed
Known_issues
- Known Issues
| Component: | Uwierzytelnianie AD | Opis | W niektórych środowiskach po aktualizacji do wersji 14.1.3 uwierzytelnianie AD może przestać działać, mimo że status połączenia nadal wskazuje, że jest aktywne (zielona kontrolka). | Solution: | Two solutions:
|
| Component: | Aktualizacje w klastrze | Opis | W związku ze zmianą sposobu przetwarzania haseł w klastrach może się zdarzyć, że zarówno główny, jak i rezerwowy moduł UTM przejdą jednocześnie w tryb aktywny. | Workaround: | Aby uniknąć tej sytuacji, zalecamy następujące postępowanie:
|
| Component: | Proxy odwrotny w nginx | Opis | Proxy odwrotny może napotkać błąd i przestać przetwarzać żądania | Workaround: | Powrót do wersji 14.0.12 lub wcześniejszej (Ponowne uruchomienie zapory lub usługi pomaga tylko tymczasowo) |
| Component: | spDYN update without IPv6 | Opis | spDYN does not update when both IPv4 and IPv6 are supposed to be updated, but there is no IPv6 available | Workaround: | Disable spDyn update, select IPv4 only option and re-enable it |
Build 14.1.2.1 Wersja beta
- Release Date: 24.02.2026
- Planowany przedział czasowy wdrożenia: 1 dzień
- Dostępne wyłącznie dla urządzeń z włączoną funkcją aktualizacji beta
Głównym celem tych wersji jest uzyskanie cennych opinii od naszych partnerów. Opinie te zostaną uwzględnione w ostatecznej wersji naszego oprogramowania, zanim zostanie ono udostępnione dla wszystkich użytkowników.
Dziękujemy wszystkim partnerom za wsparcie i wkład w optymalizację naszego oprogramowania.'
Ta wersja nie jest przeznaczona do użytku w środowiskach produkcyjnych
Action required:
From March 1, 2026, email classification will only be provided for UTM systems with supported versions.
- With UTM version 14.0.12, we are providing a technically necessary update that ensures continued proper connection to the email classification service.
This is necessary for reliable detection of spam, phishing, and, in some cases, viruses. - Technical changes have been implemented on the backend as part of an adjustment to the service interface.
- To continue using email classification, it is therefore necessary to run UTM on a supported version.
- After installing version 14.0.12, communication with the classification service will continue to function as usual, and incoming emails will be analyzed and categorized as usual.
Therefore, please update to version 14.0.12 by February 28, 2026, at the latest, to ensure continued use of the function without restrictions.
Other changes in this version:
- Maintenance / Security Bugfix
- Update of a Mailfilter component (CVE-2026-25646 / EUVD-2026-7050)
Build 14.1.2 Wersja beta
- Release Date: 12.02.2026
- Planowany przedział czasowy wdrożenia: 1 dzień
- Dostępne wyłącznie dla urządzeń z włączoną funkcją aktualizacji beta
Głównym celem tych wersji jest uzyskanie cennych opinii od naszych partnerów. Opinie te zostaną uwzględnione w ostatecznej wersji naszego oprogramowania, zanim zostanie ono udostępnione dla wszystkich użytkowników.
Dziękujemy wszystkim partnerom za wsparcie i wkład w optymalizację naszego oprogramowania.'
Ta wersja nie jest przeznaczona do użytku w środowiskach produkcyjnych
- Maintenance
- Update of the operating system and all components
- Update of OpenVPN to version 2.6.17 (CVE-2025-13086 / EUVD-2025-201102)
- Update of the name server service (CVE-2025-11411 / EUVD-2025-35360)
- Update of a mail filter component
(CVE-2026-22695 / EUVD-2026-2420),
(CVE-2026-22801 / EUVD-2026-2416) - Update of the Securepoint VPN client installer to version 1.0.1
- Update of the mail relay to Postfix version 3.10.7
- New features
- Multi-factor authentication (MFA) with Entra ID via SSL VPN (OpenVPN) is now possible with the help of OpenID Connect
- Features
- The interface assignment and appliance widget have been updated for RC300S G6
- When creating a new configuration profile in the HTTP proxy, the values of the global profile are adopted
- In the nginx reverse proxy, there is an option to enable forwarding of the SNI to the upstream server
- The lifetime for auth tokens can be set for OpenVPN roadwarriors to reduce OTP queries for new connections
- For blocks via GeoIP, the log entry now contains the corresponding country code
- The color blindness mode is applied immediately after login
- The clientless VPN dialog now provides clearer warnings about the lack of security in VNC and RDP connections and suggests optimization options
- MSS clamping for IPv6 has been added
- Bug fixes
- Minor bugs when adding options when setting up a DHCP pool have been fixed
- Domains with umlauts can now also be configured in similarity detection
- Ping check IP fallback routes are no longer considered as internal targets for the HTTP proxy ACL. This means that access to public ping check addresses remains possible even if proxy access to internal destinations is disabled
- When creating a mail connector service, newly added OAuth connections are now correctly transferred to the input mask
- For WWAN/LTE connections, the associated rules are now created completely
- Dynhost rules once again reliably support very long host names
- When creating new network objects, the zone is correctly preselected
- GeoIP network objects are no longer offered for selection in the packet filter during NAT configuration
- The behavior of sites with deny ACLs has been improved
- ACLs containing a space are added correctly
- Creating new users works reliably again
- Registration via the captive portal is working reliably again
- IP validation has been improved
- Fixed a bug in the HTTP Proxy related to Basic Authentication and Captive Portal
Build 14.1.1 Wersja beta
- Release Date: 18.11.2025
- Planowany przedział czasowy wdrożenia: 1 dzień
- Dostępne wyłącznie dla urządzeń z włączoną funkcją aktualizacji beta
Głównym celem tych wersji jest uzyskanie cennych opinii od naszych partnerów. Opinie te zostaną uwzględnione w ostatecznej wersji naszego oprogramowania, zanim zostanie ono udostępnione dla wszystkich użytkowników.
Dziękujemy wszystkim partnerom za wsparcie i wkład w optymalizację naszego oprogramowania.'
Ta wersja nie jest przeznaczona do użytku w środowiskach produkcyjnych
- Maintenance
- Update of the kernel to version 6.6
- Update of the HTTP Proxy (Squid) (CVE-2025-62168 / EUVD-2025-34894)
- Fix for a security vulnerability in the IPSec service (CVE-2025-62291)
- Updates to the appliance images for expansion slots with 2 ports
- New Features
- Similarity Detection (Experimental Feature )
- To minimize phishing attacks and fraud attempts in the Web Filter and Mail Filter, suspicious domains that show a strong similarity to known trusted domains can be marked and/or blocked. Trusted domains can be added individually in the new application menu for similarity detection.
- A domain can be tested against the Similarity Detection via the Network Tools and via the CLI
- A dialog shown at login explains the new feature and points to the corresponding menu entry
- Features
- USC Zero Touch
- Before Zero Touch enrollment of a UTM via the USC, an automatic update to the current UTM version is now performed if a configuration has been uploaded
- The UTM console and the USC display the individual steps of the enrollment process in detail
- Clientless VPN
- When configuring a connection, user groups can now be selected directly and displayed in the table
- If a connection is opened using the “Advanced Fullscreen” button, ESC can be used on the connected device
- The overview table of connections has been extended with several additional information fields
- SSL VPN
- The previous VPN Client (version 2.0.45) has been replaced by version 1.0 of the new VPN Client Installer (for client version 3.3.3)
- Mailrelay
- Outgoing IP addresses can now be specified separately for IPv4 and IPv6
- In the Mail Relay, a new switch Resolve unknown numeric domains has been added to prevent rejection by the mail relay
- Administration Interface
- The statistics widgets on the dashboard now offer more and improved interaction and analysis options
- In the Reverse Proxy and the Network Topology, nested tables can now be sorted independently
- Different HTTP Proxy configurations can now be created for different internal networks
- The modal Network Tools dialog has been improved (tooltip, accessibility via the search function, inclusion in the UTM tour, saving of the window position)
- In the Network Configuration, all standardized DHCP options can now be configured when setting up a DHCP pool
- By double-clicking the drag-and-drop icon of a table entry, the desired target position can be entered directly
- A confirmation dialog now always appears when opening external links
- The download process for multiple local configurations has been revised and made more intuitive
- In the Reverse Proxy, server groups and sites are now displayed in a single combined table
- To better distinguish between multiple open UTM interfaces, the browser title now includes information about the hostname and version while logged in (full version in the Admin UI, major version in the User UI). If the user is not logged in, only the major version is shown and no hostname
- Additional Features
- When assigning a PIN for access to the Unified Security Console, only the relevant patterns are now displayed for PINs classified as weak
- The process for creating a support user has been optimized and aligned with similar workflows
- When creating packet captures, a tooltip now points out the functionality of the slider for name resolution
- In the Packet Filter, a warning triangle indicates a potential source of error when a node with a hostname is used in a port forwarding rule
- The Mail Filter has been extended with new rule options to control how encrypted and unencrypted archives in incoming emails are handled
- The button for importing an additional configuration in the Cloud Backup is now grayed out once the maximum number of 20 configurations is reached
- Notifications from devices with eMMC storage are now also sent via the Alerting Center
- Deprecated key lengths (1024-bit and below) and ciphers (SHA1) are temporarily accepted again. This allows the HTTP Proxy and SSL VPN to continue to be used
- The unloading of helpers for services used in the rule set has been removed, as helpers should only be managed through the service settings
- Bugfixes
- Inconsistencies in the behavior of the button for enabling and disabling the implied rule in the WireGuard dialog have been corrected
- When importing a WireGuard configuration, the MTU is now read correctly
- The table search function now also finds entries in collapsed groups
- In the Reverse Proxy, issues with drag & drop and deleting entries have been fixed
- Tab completion in the CLI now correctly shows all available commands and options again during multi-line input
- The warning message for static DHCP leases at login has been adjusted
- When a hostname was used instead of an IP address, logs were sometimes not sent to the Syslog server after a reboot
- The description field of Packet Filter rules is now correctly included when downloading the configuration file as a PDF
- Transparent rules in the HTTP Proxy/POP3 Proxy always require the selection of a destination network object
- The log of the DynDNS function for a network interface is now evaluated correctly
- The legend of the email statistics in the User UI is now easier to read in dark mode
- Before reboot and rollback/dry run, the user is now properly logged out again
- A bond interface can now also be configured as the outgoing IP address in the HTTP Proxy
- Issues when configuring bond interfaces across different slots have been resolved
- Support users with root privileges again have full SSH permissions
- In the Network Topology, the assignment of dynamic DHCP leases to pools is now displayed correctly again
- Performance in user configuration has been significantly improved
- A bug in automatic QoS that caused configured bandwidth limits not to be applied in version 14.1.0 Beta has been fixed
- All license-related events are once again forwarded to the Alerting Center
- In Beta version 14.1.0, the service establishing the connection to the Securepoint Cloud malfunctioned after long runtimes due to an issue with file descriptors not being closed
- When creating a Web Filter rule of type URL, wildcards and protocols are now accepted again
- Display issues in the configuration of the Smarthost in the Mail Relay have been fixed
- When using a RADIUS server to authenticate VPN connections, OTP prompts could lead to long waiting times
Known_issues
- Known Issues
| Component: | HTTP Proxy Dienst | Opis | Nach Update auf v14.1.1 tritt im http-Proxy Dienst ein Fehler auf, wenn die Authentifizierung auf Basic steht und Captive Portal aktiv ist. | Workaround: | Korrektur in der squid.conf Nur für erfahrene Benutzer empfohlen!
|
| Component: | Anlegen neuer Benutzer | Opis | Auf Maschinen, die mit einer 11.7.X installiert und von da aus schrittweise auf 14.1.1 aktualisiert wurden, lassen sich keine neuen Benutzer anlegen | Workaround: | Rollback auf 14.1.0 Falls das nicht möglich ist, kann ein root-Benutzer Änderungen in der Datenbank vornehmen. Dazu bitte ein Support-Ticket eröffnen. |
| Component: | Captive Portal | Opis | Nach dem Update auf die v14.1.1 ist keine Anmeldung mehr am Captive Portal von einem Client aus möglich | Workaround: | Korrektur im Template portal.html Nur für erfahrene Benutzer empfohlen!
|
Build 14.1.0 Wersja beta
- Release Date: 26.08.2025
- Planowany przedział czasowy wdrożenia: 1 dzień
- Dostępne wyłącznie dla urządzeń z włączoną funkcją aktualizacji beta
Głównym celem tych wersji jest uzyskanie cennych opinii od naszych partnerów. Opinie te zostaną uwzględnione w ostatecznej wersji naszego oprogramowania, zanim zostanie ono udostępnione dla wszystkich użytkowników.
Dziękujemy wszystkim partnerom za wsparcie i wkład w optymalizację naszego oprogramowania.'
Ta wersja nie jest przeznaczona do użytku w środowiskach produkcyjnych
- Maintenance
- Update of the operating system and all components
- Update of the SSL-VPN and Mail Connector components
- Update of the Bird routing daemon for the BGP and OSPF protocols (intended for complex infrastructures only).
Configuration file adjustments are required.
- New Features
- A new dialog for creating packet captures has been added
- Cloud Shield can now also be configured for UTMs via the USP
- A Cloud Shield configuration can be deleted via permissions if access through the USC is not possible
- Features
- TI Proxy
- TI Proxy now supports multiple networks
- USC
- Additional permissions can be set for editing the UTM via the USC
- If a VPN configuration or Cloud Shield configuration exists, permission for these items cannot be revoked
- Update actions via the USC are PIN-protected
- Network
- With the LTE kit, both IPv4 and IPv6 addresses can now be used for connectivity
- The DHCP section of the network configuration dialog for IPv4 and IPv6 has been redesigned to make dependencies clearer
- The cluster wizard has been revised and now also suggests WireGuard interfaces for deactivation
- In the cluster configuration, the application status on the spare is displayed more clearly
- Network tools can now be configured via a modal dialog so that the current dialog does not need to be exited
- Mailrelay
- OAuth 2.0 can be used for authentication when sending emails via smarthosts
- With SASL authentication in the mail relay, it can also be checked whether the technical sender (envelope sender) matches the authenticated user ID
- Packet Filter
- Info icons and NAT type descriptions have been added to improve understanding when editing packet filter rules
- The format of packet filter log messages in nftables has been adjusted to simplify subsequent assignment to packet filter rules
- Authentication
- When adding an ACME certificate, an alternative certificate chain can be selected to avoid issues with outdated certificates delivered by Let’s Encrypt
- ACME certificates can now be created with elliptic curve keys
- In user management, the permissions assigned to a user are displayed as icons
- The encryption dialog has been revised and options for TLS 1.3 cipher suites have been added
- Reverse Proxy
- Similar to the Squid reverse proxy, anonymization can now also be enabled in the nginx reverse proxy
- For ACL sets in the reverse proxy, it can be specified whether case sensitivity should be enforced or ignored
- Configuration Management
- After a new installation and after activating a backup, an initial password change is enforced
- Multiple configurations can be downloaded at once. The number of configurations that can be stored has been limited to 20
- Other
- Display and handling of emails in the user interface has been significantly accelerated
- Log messages can also be filtered by packet filter groups
- For IPSec connections, encapsulation of ESP packets in UDP can be enforced to avoid communication issues with VPN connections to third-party devices
- Fastdiff and SigQA functionality of the virus scanner are enabled by default to detect new threats more effectively
- In addition to the link to the wiki, the current changelog itself can also be viewed under firmware updates
- In the CLI, there is a new context menu for copying request and response
- Internationalized domain names (e.g. with umlauts) can also be entered in the web filter
- Since the IPv4 peer address in a user’s WireGuard configuration refers to the shared IP addresses from the UTM’s perspective and is therefore not exported, the tooltip explicitly points this out
- The online help has been revised
- For more consistent handling, adding and editing elements in the web filter and mail relay dialogs have been moved into separate dialogs
- The HTTP proxy statistics in the Admin UI have been completely revised and expanded
- Bugfixes
- When the UTM is reset to factory settings, a new Zero Touch Enrollment PIN is automatically generated
- Entra integration works reliably even after multiple deactivations and reactivations
- All errors that may occur when applying a cloud backup are caught and displayed
- Issues when moving packet filter rules and groups have been fixed
- When a service on a spare UTM is explicitly stopped, the tooltip displays this correctly
- The synchronization status in a cluster is always reliably displayed on both cluster UTMs
- Special characters in passwords no longer cause problems in cluster communication
- Arguments in the CLI may now also include equal signs
- If the CA certificate for SSL interception of the HTTP proxy is changed, connections can be successfully established with the new certificate
- The save button now reliably indicates every pending change
- Deleted Entra ID users are permanently removed and not just marked as deleted
Known_issues
- Known Issues
| Component: | email archive | Opis | In the email archive, messages are currently counted incorrectly, causing too many (partly empty) pages and incorrect hit counts in the filters to be displayed | Workaround: | - |
| Component: | SIP module | Opis | If packet filter rules exist with the sip service (SIP helper) and the corresponding SIP helper modules have been disabled debug kmod unload module nf_x_y As a result, the UTM may become unreachable. |
Workaround: | Remove the required SIP helper modules from the block list via the CLI. The command debug kmod delete removes the modules from the block list after a reboot. This allows them to be loaded automatically by the packet filter rule if necessary. The error no longer occurs. cli> debug kmod delete module nf_nat_sip debug kmod delete module nf_nat_h323 debug kmod delete module nf_conntrack_sip debug kmod delete module nf_conntrack_h323 OK cli>sytem reboot |
| Component: | HTTP-Proxy / SSL-VPN | Opis | Keys that are 1024 bits or smaller or created with sha1 are not accepted. This can result in services that use such keys not working. Constant restarting increases the load, so that the UTM becomes unusable after a while (<½h). |
Workaround: | Replace all old, insecure keys with current keys with the recommended length of 3072 bits or longer. |
| Component: | QoS | Opis | Configured automatic QoS does not apply the stored settings | Workaround: | - |
Build 14.0.12
- Release Date: 19.02.2026
- Planowany przedział czasowy wdrożenia: 4 dni
- Terra Cloud: 19.02.2026
- Planowany przedział czasowy wdrożenia: 4 dni
Action required:
From March 1, 2026, email classification will only be provided for UTM systems with supported versions.
- With UTM version 14.0.12, we are providing a technically necessary update that ensures continued proper connection to the email classification service.
This is necessary for reliable detection of spam, phishing, and, in some cases, viruses. - Technical changes have been implemented on the backend as part of an adjustment to the service interface.
- To continue using email classification, it is therefore necessary to run UTM on a supported version.
- After installing version 14.0.12, communication with the classification service will continue to function as usual, and incoming emails will be analyzed and categorized as usual.
Therefore, please update to version 14.0.12 by February 28, 2026, at the latest, to ensure continued use of the function without restrictions.
Other changes in this version:
- Maintenance / Security Bugfix
- Update of a Mailfilter component (CVE-2026-25646 / EUVD-2026-7050)
Build 14.0.11
- Release Date: 03.02.2026
- Planowany przedział czasowy wdrożenia: 7 dni
- Terra Cloud: 11.02.2026
- Planowany przedział czasowy wdrożenia: 3 dni
- Security Bugfix / Maintenance
- Update of a Mailfilter component (CVE-2026-22695 / EUVD-2026-2420) / (CVE-2026-22801 / EUVD-2026-2416)
- Update of OpenSSL (CVE-2025-15467 / (EUVD-2025-206379)
Build 14.0.10
- Release Date: 07.01.9026
- Planowany przedział czasowy wdrożenia: 7 dni
- Terra Cloud: 13.01.2026
- Planowany przedział czasowy wdrożenia: 3 dni
- Security Bugfix / Maintenance
- Update of nameserver service (CVE-2025-11411)
Build 14.0.9.2
- Release Date: 04.11.2025
- Planowany przedział czasowy wdrożenia: 7 dni
- Security Bugfix / Maintenance
- The clientless VPN dialog now provides clearer warnings about the lack of security of VNC and RDP connections and possible optimization options
- Hardening of clientless VPN security
- Fixing a security vulnerability in the IPSec service (CVE-2025-62291)
Build 14.0.9.1
- Release Date: 22.10.2025
- Planowany przedział czasowy wdrożenia: 7 dni
Update of http proxy (squid) (CVE-2025-62168 / EUVD-2025-34894)
Build 14.0.9
- Release Date: 07.10.2025
- Planowany przedział czasowy wdrożenia: 14 dni
- Feature
- The TI Proxy now supports terminals connected to different local networks
- Bugfixes
- Fixed an issue where VLAN interfaces were created incorrectly when updating from version 14.0.6 to 14.0.7.1
- Fixed errors when starting cloud backups after a license exchange
- UTMs without network object groups can now be integrated into a VPN configuration in the USC
- License terms in firmware updates are now displayed without delay
- Dropdown menus and emails in the user interface are now more readable in dark mode
Known_issue
- Known Issue
| Component: | OpenVPN / SSL-VPN | Opis | We are currently investigating issues with OpenVPN Roadwarrior tunnels using Radius authentication. | Workaround: | - |
Build 14.0.8.2
- Release Date: 18.08.2025
- Planowany przedział czasowy wdrożenia: 7 dni
- Maintenance / Security
- Update libarchive to version 3.8.1 (CVE-2025-5914 / EUVD-2025-17572)
- Bugfix
- Fixes an ssue in the TI proxy that caused updates to fail on card terminals in some circumstances
Build 14.0.7.1
- Release Date: 16.07.2025
- Planowany przedział czasowy wdrożenia: 14 dni
- Features
- Accurate diagrams for new UTM models have been added
- If the delivery password has not yet been changed, the password change is now forced during the web interface login
- Bugfixes
- The risk that the Zero Touch Enrollment PIN is not saved during an uncontrolled reboot/shutdown during installation has been minimised.
If the PIN is still lost, a new PIN is generated and displayed on the UTM console
Build 14.0.6
- Release Date: 12.06.2025
- Planowany przedział czasowy wdrożenia: 14 dni
- Features
- Accurate diagrams for new UTM models have been added
- Potentially security-critical data in the configuration report is now unrecognisable
Known_issues
- Known Issues
| Component: | Zero-touch enrollment PIN | Opis | When resetting to factory settings, the enrollment PIN for Zero-Touch is not regenerated | Workaround: | A new enrollment PIN is generated during a complete reinstallation via USB stick |
Build 14.0.5
- Release Date: 21.05.2025
- Planowany przedział czasowy wdrożenia: 14 dni
- Maintenance
- VPN Client has been updated to 2.0.44
- Features*
- The name of the configured certificate is now displayed in the sites table of the reverse proxy dialogue. In case of warnings, this name is highlighted in red and is provided with an explanatory tooltip
- There is a new note to the user that a restart of the UTM is necessary to fully activate a configuration
- Bugfixes
- Temporary files in the nginx reverse proxy are now reliably deleted regularly to avoid excessive memory consumption
- When deactivating the transparent mode in the HTTP proxy, the error 'error in implied rules' is now prevented
- When creating packet filter rules, an incorrectly saved empty string overwrote the ID with an empty log alias
- The nginx version used was removed from the reverse proxy header for security reasons
- Rules created and deleted via the USP no longer cause rules to be displayed in the wrong groups in the frontend
- Rule-based routing is once again correctly evaluated before tunnel routes in SSLVPN site-to-site tunnels
Build 14.0.4
- Release Date: 15.04.2025
- Planowany przedział czasowy wdrożenia: 14 dni
- Features
- A new wizard simplifies the configuration of a TI proxy connection
- In the cluster configuration, a tooltip explains the use of the remote peer's SSH key
- The user is now more clearly informed of possible misconfigurations when configuring the reverse proxy
- Bugfixes
- In rare cases, valid domains were blocked by the HTTP proxy
- Very rarely problems occurred when establishing the web session via the Unified Security Portal
- Display problems when switching from and to the packet filter dialogue have been fixed
- If inconsistencies occur in the VPN configuration via the Unified Security Portal, these are now intercepted more smoothly in the backend and packet filter UI
- Display problems with the protected addresses in the DNS rebind prevention of the name server have been fixed
- A UTM now obtains an IP via DHCP again after a restart, even if a fallback is configured on an external interface
Build 14.0.3
- Release Date: 26.03.2025
- Planowany przedział czasowy wdrożenia: 14 dni
- Features
- There is a new extc variable ‘MAXLEASES’ for setting the maximum number of DHCP leases via the advanced settings
- The default value for the encryption algorithm (‘Cipher for data connection’ field) for SSL VPN connections has been updated to AES-256-GCM
- The login screen for the new Luna design has been adapted to the existing layout
- Bugfixes
- The mouseover text for the target port for services in the packet filter has been corrected
- Changes to the DHCP relay settings made via the configuration interface are now applied correctly
- The error message when moving rules and rule groups in the packet filter is now more informative
- The DHCP client now always requests a new IP address after an interface update to ensure a seamless connection when changing the network
- After switching off the HTTP proxy, devices from the internal network can still access the Internet according to the configured rules
- Even if a WireGuard connection has been created via the cloud, additional local WireGuard tunnels can now be added
- The name of a local configuration for cloud backups may now also contain umlauts
- The tab completion in the CLI is available again
- The HTTP proxy statistics correctly fill the entire popup window again
- Display problems in the e-mail administration have been fixed
- Ordered lists are displayed correctly again in e-mail details
- Icons on buttons are displayed reliably again in the admin interface
- The values from the extc variable CHALLENGE_DNS_SERVERS are now retained during updates
- In rare cases there were connection problems to the USC due to missing updates from the license server. These problems have been fixed
Known_issues
- Known Issues
| Affected component | Opis | Workaround |
|---|---|---|
| HTTP Proxy as of v14.0.2 |
Problems with unsupported protocols An update of the Squid engine leads to an error with unsupported protocols. |
Create exclude rule in HTTP proxy Under przycisk create a network object with the type: . Specify the site that leads to the error as the host name.
At Obszar Transparenter Modus przycisk If this does not help, please open a support ticket. |
| DHCP service | An interface does not receive an IP address via DHCP if a fallback is configured at the same time. | Assign a fixed IP address on the interface. |
Build 14.0.2
- Release Date: 26.02.2025
- Planowany przedział czasowy wdrożenia: 14 dni
- Maintenance / Security Bugfixes
- Mail relay has been updated to Postfix version 3.7.12
- SSH service has been updated to version 9.9p2 (CVE-2025-26465), (CVE-2025-26466)
- Features
- New popup window during login to activate the use of beta versions
- The login screen has been adapted to the new Luna design
- Bugfixes
- Fixed an internal error that prevented administration via Admin UI/CLI in some cases
- Virus findings in the HTTP proxy are reported via the Alerting Center again
- The MIME type blocklist in the HTTP proxy has been optimised
- Mails containing links with incorrectly formatted href tags are no longer temporarily rejected
- The log level for timeouts in the mail scanner has been reduced from ERROR to INFO in order to reduce unnecessary warnings via the Alerting Center
- When importing a new licence file via the web session, a message is now displayed that the web session window will be closed and the session will expire shortly afterwards
- Fixed a bug that prevented the addition of an Ethernet interface
- IPSec tunnel networks were sometimes displayed incorrectly if the corresponding tunnel was not established
- In addition, all changes from the Reseller Previews and Beta Versions are included:
- Maintenance
- This version is distributed as a beta version
It is only available for versions with the Reseller Preview v14.0.1 and activated beta updates - Update of the operating system and all components
- DHCP transition widget has been removed
- Maintenance / Security / Operating System
- Update of the Squid service
- DNS has been updated with a new service with additional functions
- Feature
- New Features:
- Reseller previews are replaced by the beta program and can now be downloaded optionally
- As of the upcoming USP Portal 2.0 beta, VPN configurations can be published on appliances
- VPN configuration from the USC can be deactivated in the USP dialog
- Alert added if a database conversion problem occurs during a configuration import
- Connection of card terminals is possible with the new TI proxy
- New wizard for cluster configurations available
- Administration web interface:
- Wireguard connections can now be deactivated
- E-mail management has been optimized in the user interface
- DNS Forwarding can now be configured in the installation wizard
- Tables can now be displayed in additional styles, have paging, maximum height settings and an associated configuration menu
- A new dialog for configuring the global table settings has been added to the navigation
- For expandable tables, which entries are expanded is persisted
- Tables retain their scroll position and their current page even when reloaded
- Tables are now loaded much more efficiently - especially when paging is active
- It is ensured that cell contents are always in the visible area when scrolling
- extc Runtimevars can be viewed in the advanced settings
- Interface options for duplex and speed are always visible
- The applied filter rule/selector is now also displayed for accepted mails
- Multiple NTP servers are configurable
- General system information and log files can be downloaded as a compressed file directly in the support user dialog
- The source IP can be selected in the traceroute network tool
- Warnings about unsynchronized clusters are displayed
- Rules can be assigned aliases that can be used to filter the weblog
- Display of inherited user authorizations has been extended
- The MDNS repeater now has its own menu entry in the applications
- The mail filter can now be activated in more dialogs
- Automatic generation of OTP codes has been optimized
- Multiple emails can be selected and tagged simultaneously in the user interface (#39176)
- The tour has been moved to the configuration dialog
- Alerting Center:
- Alerts are displayed in the top right of the admin interface
- Alerts for bond interface events have been added
- Other:
- The CLI via SSH has a persistent history
- IP addresses for the ACL type “dstdomain” can be set again for reverse proxy
- New SNMP OIDs for monitoring the cluster status have been added
- VPN configurations can be downloaded with embedded certificates
- Geo IP blocking has been moved to the IDS / IPS menu
- System-wide blocking of IP addresses is now available under IDS / IPS-->
- ACLs in the reverse proxy are now validated
- Wireguard interfaces are marked and deactivated for cluster spares in backup mode
- Fallback interfaces are only used as fallback if they are also online
- Grouping of subnet combinations can be deactivated in the IPSec Wizard
- Cluster dialog has been redesigned
- Bugfixes
- Update finalization messages have been removed from syslog when the Unified Security Report is enabled
- VPN configurations set up via Unified Security Console are now completely deleted
- Loading times of the HTTP proxy dialog have been optimized
- Wake on LAN (WOL) has been further optimized
- Fixed incorrect behavior of the Alerting Center test report function
- Sorting of network objects in the administration web interface has been optimized
- Under certain circumstances, the clipboard was no longer functional for clientless VPN connections
- SASL authentication was activated on the mail relay even if no users had the corresponding rights
- Search in email management is now case insensitive
- Nginx reverse proxy responds to non-existent pages with status code 403 instead of 500
- DHCP pool customization via SPCLI was only executable once
- Fixed a bug that caused an incomplete DHCP relay configuration to be created after restart
- The vendor options were not processed correctly on the DHCP server under certain circumstances
- A memory leak in the SSL interception function of the HTTP proxy has been fixed
- WLAN widget no longer worked correctly
- The spupdater service could not process the update server status message correctly
- Central service of the firewall generated a segfault
- HTTP Proxy service did not start if invalid regex entries were configured
- Minor visual user interface bugs and hints have been adjusted
- No new license could be imported via a web session
- Inheritance of group permissions and attributes has been revised
- Virtual IPs were not removed correctly when reconfiguring clusters
- Error message in case of failed cluster synchronization with different UTM versions has been revised
- Web sessions could be canceled under certain circumstances if the appliance responded with a delay
- Unnecessary alarm messages on unopened ports with nftables have been fixed
Known_issues
- Known Issue
| Affected component | Opis | Workaround |
|---|---|---|
| DHCP-Server | The service for the DHCP server is limited to 1000 leases by default. If this number is reached without older leases being unlocked, no more DHCP leases are distributed. |
Open a ticket in Support to edit a template |
| VPN | If a WireGuard connection has been created via the cloud, no further local WireGuard tunnels can be added | - |
| Cloud-Backup | An umlaut (ä, ö, or ü) in the name of the local configuration prevents a successful cloud backup. | |
| ACME Certificate Update | After updating to 14.0.1 or 14.0.2, problems may occur in the ACME certificate update if the “system-wide name servers for ACME challenges” were not used. The reason for this is an error in the update script, which deletes values from the extc variable CHALLENGE_DNS_SERVERS. |
Menu Obszar ACME Option Use system-wide nameservers for ACME challenges {{#var\:no}} disable and enter the original value in the click box »203.0.113.113 under the option Nameservers for ACME Challenges. ( Adjust the IP address!) (See also the wiki on ACME Certificates) Alternatively: |
Build 14.0.1.1 Wersja beta
- Release Date: 11.02.2024
- Planowany przedział czasowy wdrożenia: 1 dzień
- Dostępne wyłącznie dla urządzeń z włączoną funkcją aktualizacji beta
Głównym celem tych wersji jest uzyskanie cennych opinii od naszych partnerów. Opinie te zostaną uwzględnione w ostatecznej wersji naszego oprogramowania, zanim zostanie ono udostępnione dla wszystkich użytkowników.
Dziękujemy wszystkim partnerom za wsparcie i wkład w optymalizację naszego oprogramowania.'
Ta wersja nie jest przeznaczona do użytku w środowiskach produkcyjnych
- Maintenance
- This version is distributed as a beta version
It is only available for versions with the Reseller Preview v14.0.1 and activated beta updates
- Bugfixes
- Update finalization messages have been removed from syslog when the Unified Security Report is enabled
- VPN configurations set up via Unified Security Console are now completely deleted
- Loading times of the HTTP proxy dialog have been optimized
Known_issue
- Known Issue
| Affected component | Opis | Workaround |
|---|---|---|
| Admin interface: Creating Ethernet interfaces | When creating Ethernet interfaces, the UI may no longer respond to inputs | Creating interface with the CLI |
Build 14.0.1 Reseller Preview
- Release Date: 30.01.2024
- Planowany przedział czasowy wdrożenia: 1 dzień
- Available only für devices with nfr license
These Reseller Previews are beta versions of our software. The main intention of these versions is to receive valuable feedback from our partners. This feedback is incorporated into the final version of our software before it is delivered to end customers.
We would like to thank all our partners for their support and their contributions to the optimisation of our software.
This version is not intended for use in production environments
- Maintenance
- Update of the operating system and all components
- DHCP transition widget has been removed
- New Features:
- Reseller previews are replaced by the beta program and can now be downloaded optionally
- Administration web interface:
- Wireguard connections can now be deactivated
- E-mail management has been optimized in the user interface
- DNS Forwarding can now be configured in the installation wizard
- Other:
- The CLI via SSH has a persistent history
- IP addresses for the ACL type “dstdomain” can be set again for reverse proxy
- New SNMP OIDs for monitoring the cluster status have been added
- VPN configurations can be downloaded with embedded certificates
- Geo IP blocking has been moved to the IDS / IPS menu
- System-wide blocking of IP addresses is now available under IDS / IPS-->
- Bugfixes
- Wake on LAN (WOL) has been further optimized
- Fixed incorrect behavior of the Alerting Center test report function
- Sorting of network objects in the administration web interface has been optimized
- Under certain circumstances, the clipboard was no longer functional for clientless VPN connections
- SASL authentication was activated on the mail relay even if no users had the corresponding rights
- Search in email management is now case insensitive
- Nginx reverse proxy responds to non-existent pages with status code 403 instead of 500
- DHCP pool customization via SPCLI was only executable once
- Fixed a bug that caused an incomplete DHCP relay configuration to be created after restart
- The vendor options were not processed correctly on the DHCP server under certain circumstances
Build 14.0.0.2 Reseller Preview
- Release Date: 09.12.2024
- Planowany przedział czasowy wdrożenia: 1 dzień
- Available only für devices with nfr license
These Reseller Previews are beta versions of our software. The main intention of these versions is to receive valuable feedback from our partners. This feedback is incorporated into the final version of our software before it is delivered to end customers.
We would like to thank all our partners for their support and their contributions to the optimisation of our software.
This version is not intended for use in production environments
- A memory leak in the SSL interception function of the HTTP proxy has been fixed
Known_issues
- Known Issues
| Affected component | Opis | Workaround |
|---|---|---|
| DHCP Relay v12.7.4 |
The DHCP relay does not start if a DHCP pool is not also defined. | Create any (unused) DHCP pool |
Build 14.0.0.1 Reseller Preview
- Release Date: 2.12.2024
- Planowany przedział czasowy wdrożenia: 1 dzień
- Available only für devices with nfr license
These Reseller Previews are beta versions of our software. The main intention of these versions is to receive valuable feedback from our partners. This feedback is incorporated into the final version of our software before it is delivered to end customers.
We would like to thank all our partners for their support and their contributions to the optimisation of our software.
This version is not intended for use in production environments
- WLAN widget no longer worked correctly
- The spupdater service could not process the update server status message correctly
- Central service of the firewall generated a segfault
- HTTP Proxy service did not start if invalid regex entries were configured
Known_issues
- Known Issues
| Affected component | Opis | Workaround |
|---|---|---|
| DHCP Relay v12.7.4 |
The DHCP relay does not start if a DHCP pool is not also defined. | Create any (unused) DHCP pool |
Build 14.0 Reseller Preview
- Release Date: 25.11.2024
- Planowany przedział czasowy wdrożenia: 1 dzień
- Available only für devices with nfr license
These Reseller Previews are beta versions of our software. The main intention of these versions is to receive valuable feedback from our partners. This feedback is incorporated into the final version of our software before it is delivered to end customers.
We would like to thank all our partners for their support and their contributions to the optimisation of our software.
This version is not intended for use in production environments
- Maintenance / Security / Operating System
- Update of the Squid service
- DNS has been updated with a new service with additional functions
- Feature
- As of the upcoming USP Portal 2.0 beta, VPN configurations can be published on appliances
- VPN configuration from the USC can be deactivated in the USP dialog
- Alert added if a database conversion problem occurs during a configuration import
- Connection of card terminals is possible with the new TI proxy
- New wizard for cluster configurations available
- Administration web interface:
- Tables can now be displayed in additional styles, have paging, maximum height settings and an associated configuration menu
- A new dialog for configuring the global table settings has been added to the navigation
- For expandable tables, which entries are expanded is persisted
- Tables retain their scroll position and their current page even when reloaded
- Tables are now loaded much more efficiently - especially when paging is active
- It is ensured that cell contents are always in the visible area when scrolling
- extc Runtimevars can be viewed in the advanced settings
- Interface options for duplex and speed are always visible
- The applied filter rule/selector is now also displayed for accepted mails
- Multiple NTP servers are configurable
- General system information and log files can be downloaded as a compressed file directly in the support user dialog
- The source IP can be selected in the traceroute network tool
- Warnings about unsynchronized clusters are displayed
- Rules can be assigned aliases that can be used to filter the weblog
- Display of inherited user authorizations has been extended
- The MDNS repeater now has its own menu entry in the applications
- The mail filter can now be activated in more dialogs
- Automatic generation of OTP codes has been optimized
- Multiple emails can be selected and tagged simultaneously in the user interface (#39176)
- The tour has been moved to the configuration dialog
- Alerting Center:
- Alerts are displayed in the top right of the admin interface
- Alerts for bond interface events have been added
- Other:
- ACLs in the reverse proxy are now validated
- Wireguard interfaces are marked and deactivated for cluster spares in backup mode
- Fallback interfaces are only used as fallback if they are also online
- Grouping of subnet combinations can be deactivated in the IPSec Wizard
- Cluster dialog has been redesigned
- Bugfixes
- Minor visual user interface bugs and hints have been adjusted
- No new license could be imported via a web session
- Inheritance of group permissions and attributes has been revised
- Virtual IPs were not removed correctly when reconfiguring clusters
- Error message in case of failed cluster synchronization with different UTM versions has been revised
- Web sessions could be canceled under certain circumstances if the appliance responded with a delay
- Unnecessary alarm messages on unopened ports with nftables have been fixed
Known_issues
- Known Issues
| Affected component | Opis | Workaround |
|---|---|---|
| DHCP Relay v12.7.4 |
The DHCP relay does not start if a DHCP pool is not also defined. | Create any (unused) DHCP pool |
Securepoint UTM v12
Securepoint UTM v12Securepoint UTM v11
Securepoint UTM v11
Securepoint UTM v10
Securepoint UTM v10