


Instructions for setting up an IPSec IKEv2 connection with LANCOM routers
New article: 06.2024
notempty
This article refers to a Beta version
-
Preliminary remark
The following shows how to configure an IPSec IKEv2 connection with LANCOM routers and where to find the relevant settings in the router web interface.
The following local example networks should be accessible via the S2S connection:
| Local router network | 172.30.0.0/24 |
| Shared UTM networks | 172.31.2.0/24 & 192.168.250.0/24 |
Configuration of the UTM
notempty
The connection is set up on the UTM as described in the wiki article IPSec Site-to-Site.
The following configurations are then adjusted:
The following configurations are then adjusted:
UTMuser@firewall.name.fqdnVPNIPSec 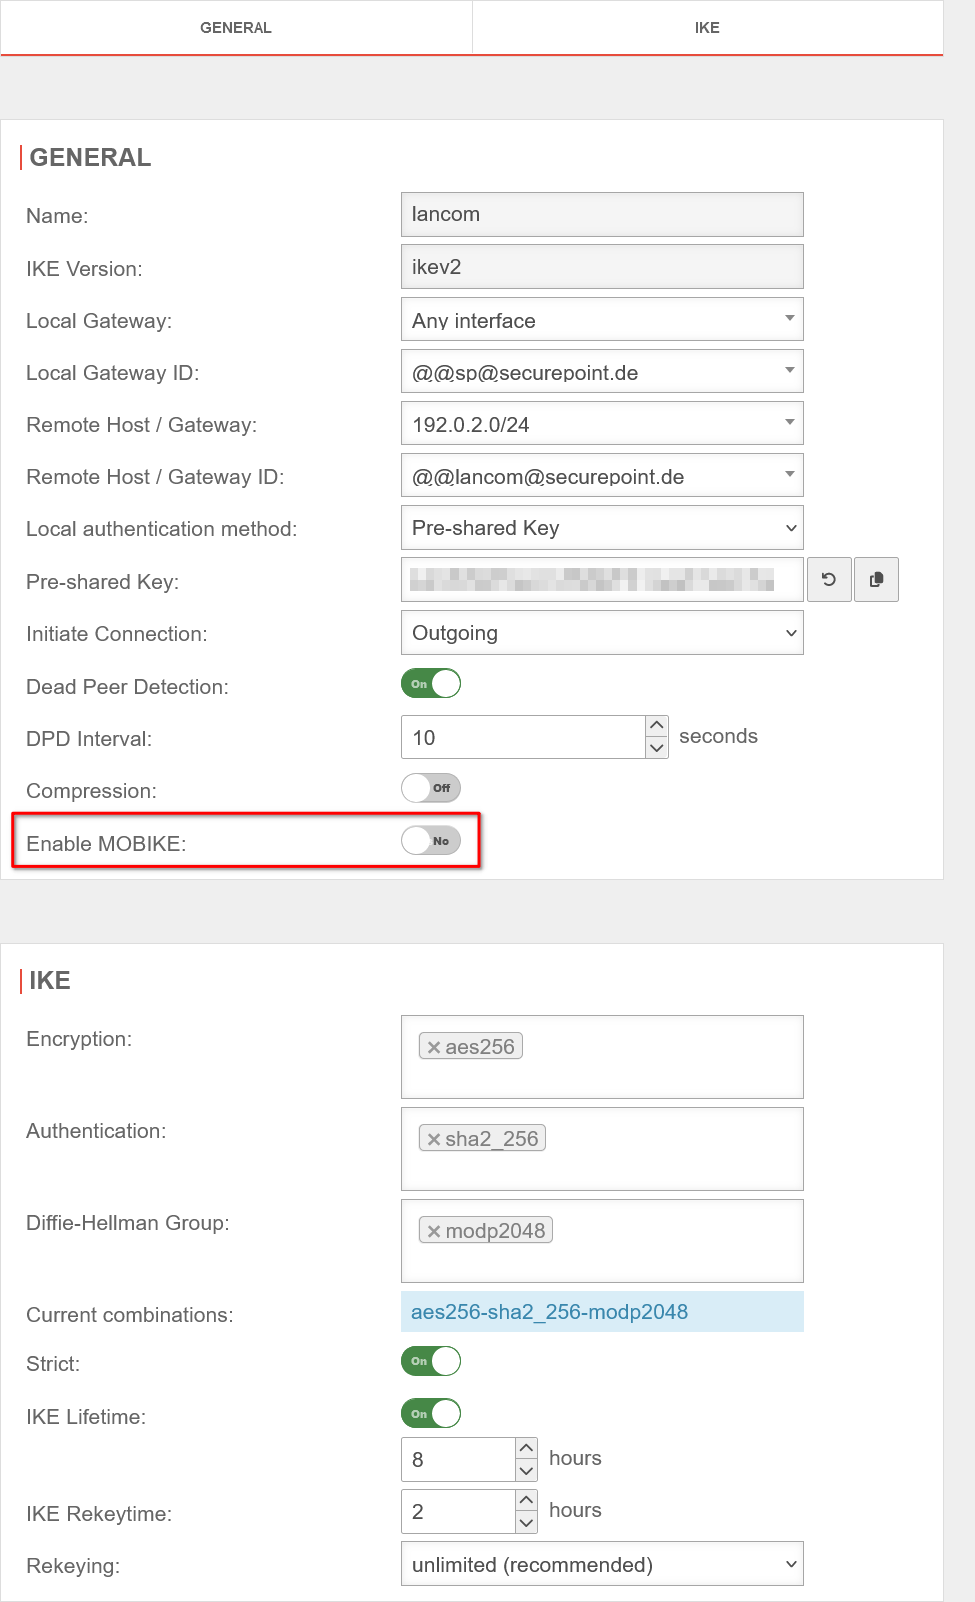

Fig.1
The following configurations must be adjusted under Area Connections button :
When using an email address as an ID, it is essential to pay attention to the double @ in front of the email address! (Example: @@mail@anyideas.de)
- MOBIKE must be deactivated
- It is also recommended with regard to gateway IDs:
- with fixed, public IPs on both sides: IP addresses
- in all other cases: Email addresses
UTMuser@firewall.name.fqdnVPNIPSec 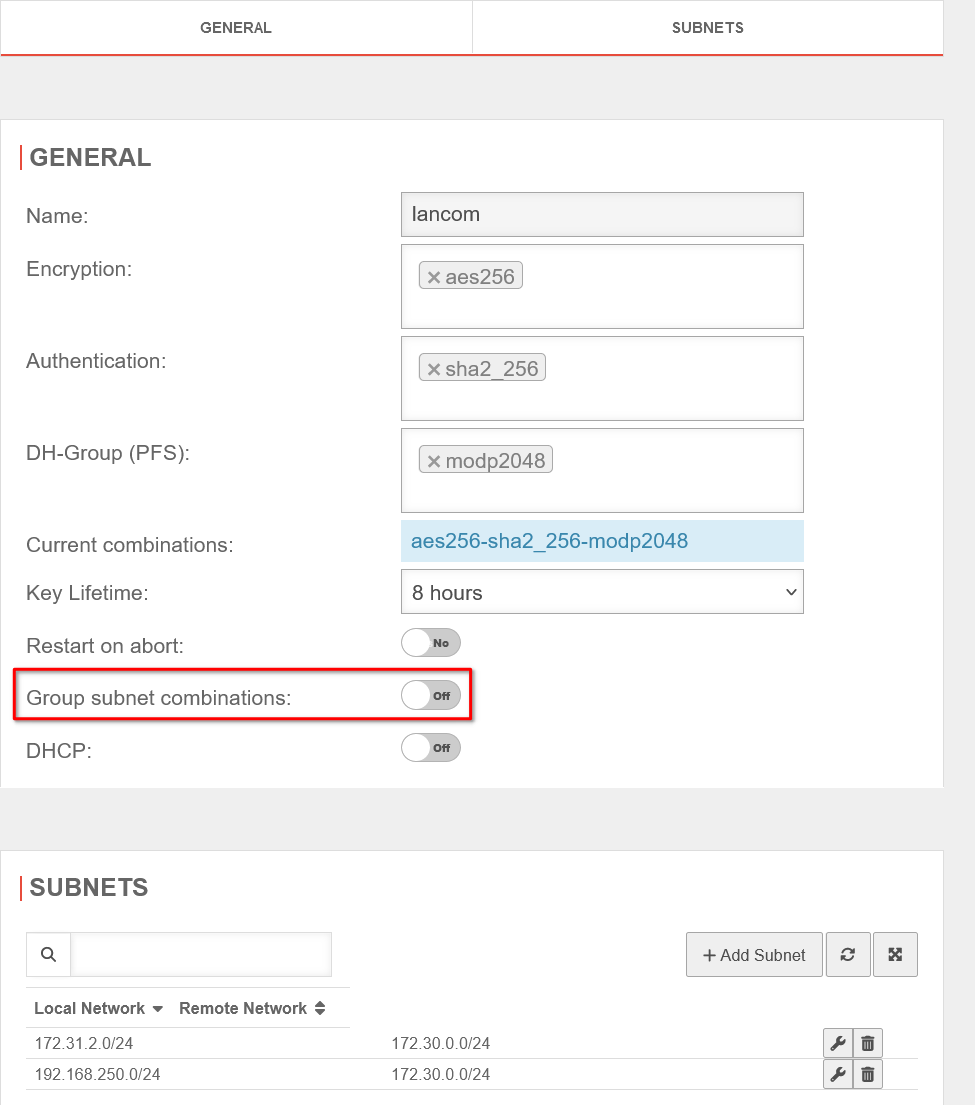

Fig.2
Under Area Connections button the grouping of subnet combinations must be switched off.
Configuration of the LANCOM router
The connection parameters are then configured on the LANCOM router.
To do this, the various data records must first be created. This is done in the web interface of the router, mainly under Configuration → VPN → IKEv2/IPSec, exceptions are the IPv4-Rules and the Routing.
The data records can always be edited by clicking on the name highlighted in blue and new data records can be created using the button, which can be found at the bottom center.
Checking/troubleshooting
| You can see whether a configured connection has been established in the dashboard in the "VPN" line (scroll down a little if necessary). | [[Datei: ]] Dashboard
|
| In addition, the actions of the router can be tracked under System information → Syslog to identify possible problems. | [[Datei: ]] Syslog
|
Location of relevant settings in the router web interface
| The following table shows where the settings known from the UTM can be configured in the web interface of the Lancom router. notempty
$NAME is a placeholder for the name of a data record that must be opened by clicking on it. | |
Phase 1GeneralGeneral
| |
| Bezeichnung Securepoint UTM | Bezeichung Lancom |
|---|---|
| Local Gateway | No suitable counterpart available |
| Local Gateway ID | Configuration → VPN → IKEv2/IPSec → Authentication → $NAME → Local identity If this is set, the remote identity type must also be set in any case! |
| Remote Host / Gateway | Configuration → VPN → IKEv2/IPSec → Connection list → $NAME → Remote gateway |
| Remote Host / Gateway ID | Configuration → VPN → IKEv2/IPSec → |
| Authentication method | Configuration → VPN → IKEv2/IPSec → Authentication → $NAME → Local authentication Configuration → VPN → IKEv2/IPSec → Authentication → $NAME → remote authentication |
| Pre-Shared Key | Configuration → VPN → IKEv2/IPSec → Authentication → $NAME → Local password Configuration → VPN → IKEv2/IPSec → Authentication → $NAME → Remote password |
| Starting behavior: Incoming | Configuration → VPN → IKEv2/IPSec → Connection list → $NAME → Hold time: 0 |
| Starting behavior: Outgoing | Configuration → VPN → IKEv2/IPSec → Connection list → $NAME → Hold time: 9999 |
| Dead Peer Detection / DPD Interval | Configuration → VPN → IKEv2/IPSec → Connection-parameters → $NAME → Dead Peer Detection |
IKEIKE
| |
| Encryption | Configuration → VPN → IKEv2/IPSec → Encryption → $NAME → IKE-SA encryption list |
| Authentication | Configuration → VPN → IKEv2/IPSec → Encryption → $NAME → IKE-SA hash list |
| Diffie-Hellman Group | Configuration → VPN → IKEv2/IPSec → Encryption → $NAME → Allowed DH groups |
| IKE Lifetime | Configuration → VPN → IKEv2/IPSec → Validity period → $NAME → IKE SA |
Phase 2GeneralGeneral
| |
| Encryption | Configuration → VPN → IKEv2/IPSec → Encryption → $NAME → Child-SA encryption list |
| Authentication | Configuration → VPN → IKEv2/IPSec → Encryption → $NAME → Child-SA hash list |
| DH Group (PFS) | Configuration → VPN → IKEv2/IPSec → Encryption → $NAME → Allowed DH groups → PFS: Yes |
| Key service life | Configuration → VPN → IKEv2/IPSec → Validity period → $NAME → Child SA |
SubnetSubnet
| |
| Local network | Configuration → VPN → General → IPv4 rules → $NAME → Remote networks |
| Remote network | Configuration → VPN → General → IPv4 rules → $NAME → Local networks |
notempty
Local on one side is always remote on the other side! | |